Trace the blast radius across repos
Multiple reviewer agents trace every change across every repo you connect, checked against your team's rules and recent commits. Each finding cites the real call chain from Niro's graph, and lands on its exact line with a fix.
Set up in three steps
Install the GitHub App
Pick the repositories. Niro never runs on one you didn't choose.
Niro indexes the repo
It builds the call graph once, then keeps it current as your branches move.
Choose the role
Advisor comments and never blocks.
Guardian blocks the merge on a blocker.
One pull request, start to finish
Every screen is a real capture of one review. Scroll through the steps, or pick one.
What the rename actually breaks
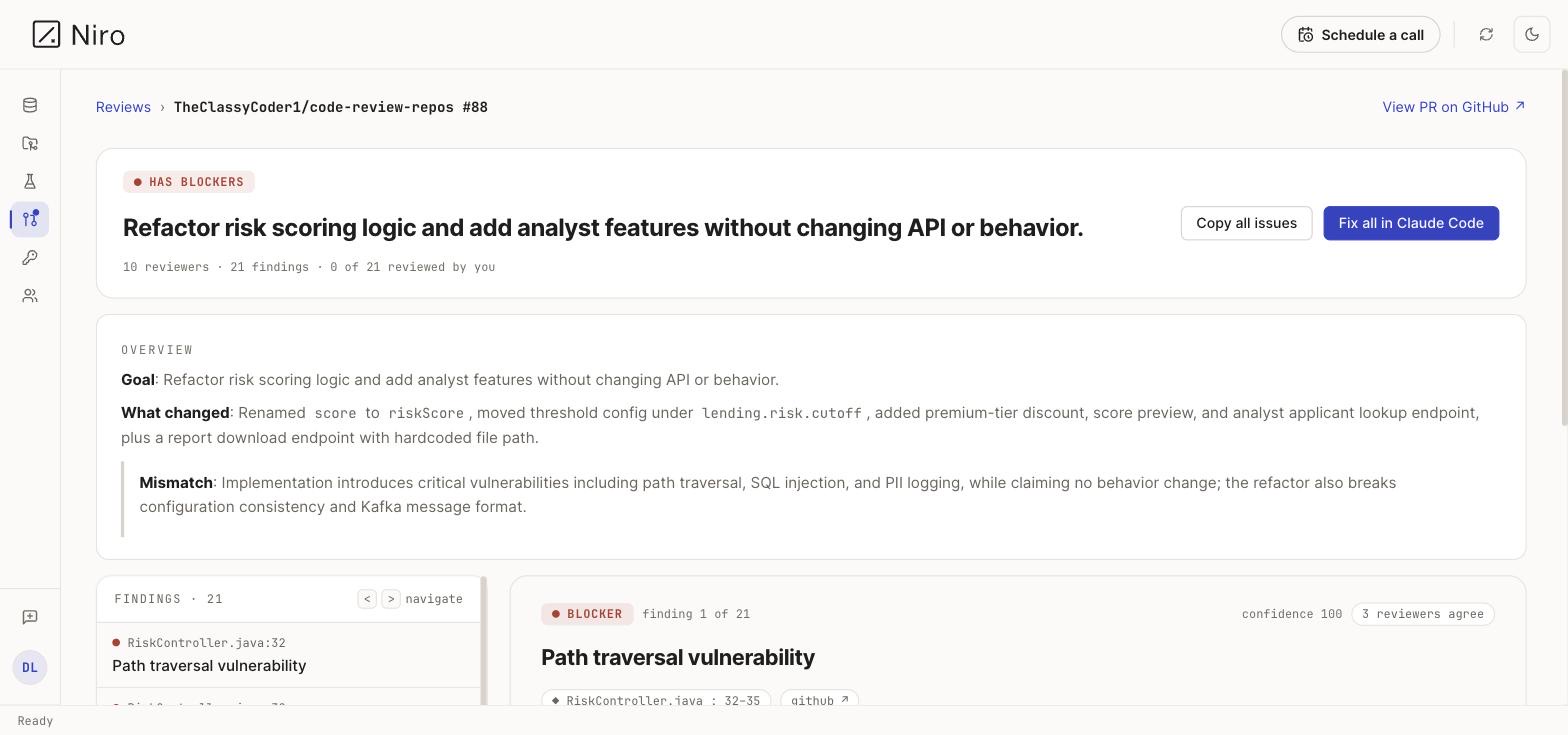
The PR renamed score to riskScore. Niro traced who still depends on it, and cited each call chain on the finding so a reviewer can check it.
What each reviewer checks for
These are findings from the same pull request, matched to the agent by the evidence each one cites.
Field renamed from score to riskScore
Names the two callers outside the diff, RiskGrpcService.assess and RiskEventConsumer.onLoanApplied, that still depend on the old field.
RiskAssessmentDto.java:5Reverted risk rejection fix
Quotes the commit "fix(risk): reject loans with a non-positive amount" that this PR quietly undoes.
DefaultRiskAssessor.java:18Configuration property rename mismatch
The key was renamed to cutoff in application.yml, but the @Value annotation still reads threshold.
DefaultRiskAssessor.java:14Risk assessment logic changed
The check moved from <= to <, while the description says "No API or behaviour change".
DefaultRiskAssessor.java:18Path traversal vulnerability
The report name goes straight into a file path. Three reviewers flagged the same lines.
RiskController.java:32PII logged in plain text
Names, emails and national IDs written to logs. Cites GDPR Art. 5(1)(f) and Art. 32.
AnalystController.java:23Exposed management endpoints
Every actuator endpoint exposed, with environment values shown in full.
application.yml:35Field injection used
Quotes the repo rule: "Use constructor injection. Do not use field injection with @Autowired."
AnalystController.java:23Reinvented JSON serialization
Hand-built JSON by string concatenation, where Jackson already does the job.
RiskEventProducer.java:22A history of every review
GitHub gets the verdict. The console keeps the history, the trends, and the controls.
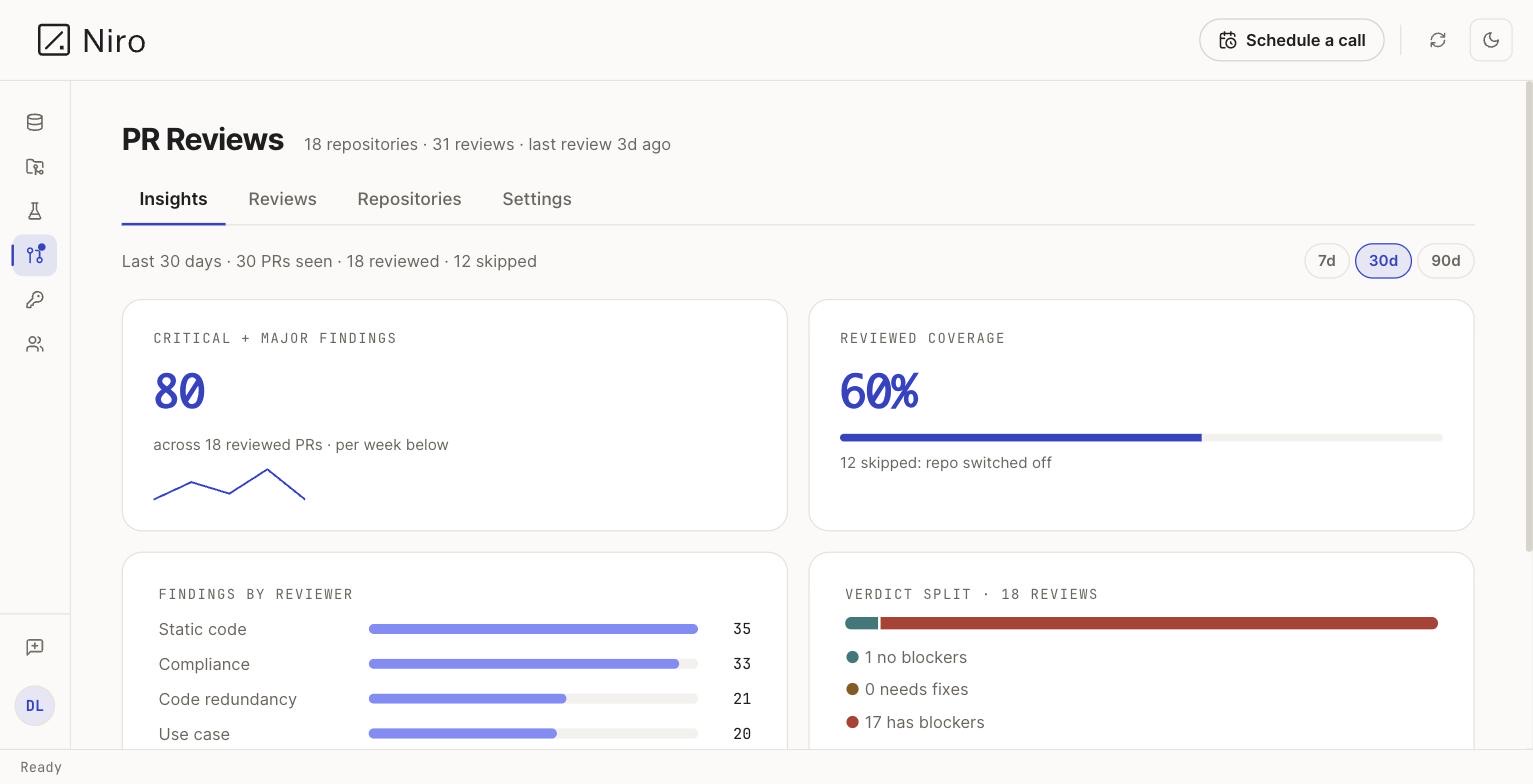
Trends across every reviewed PR
Critical and major findings per week, how many PRs were reviewed, which reviewers find the most, and how verdicts split.
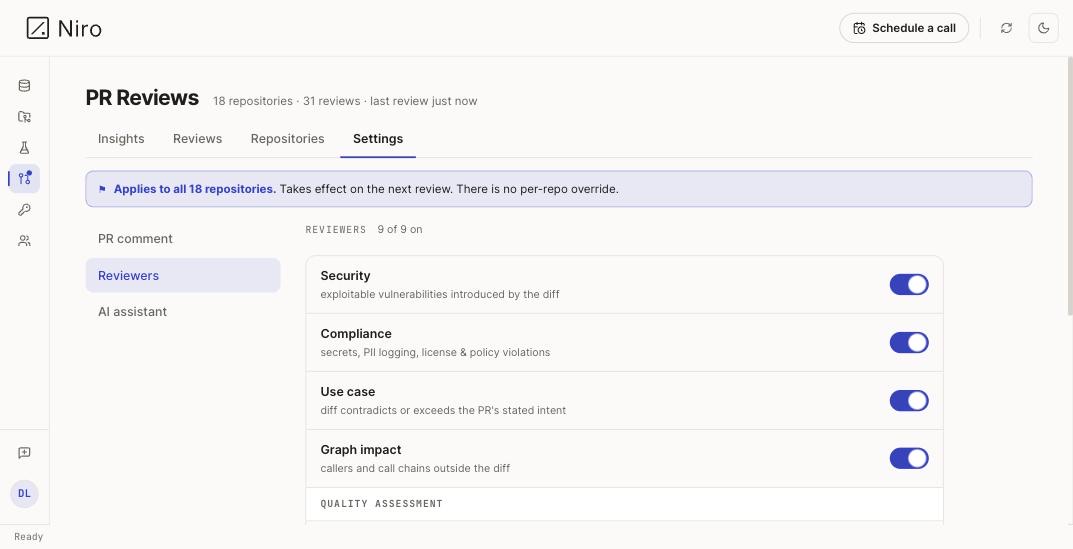
Switch reviewers on and off
Turn on the reviewers that match how your team ships. Changes apply from the next review.
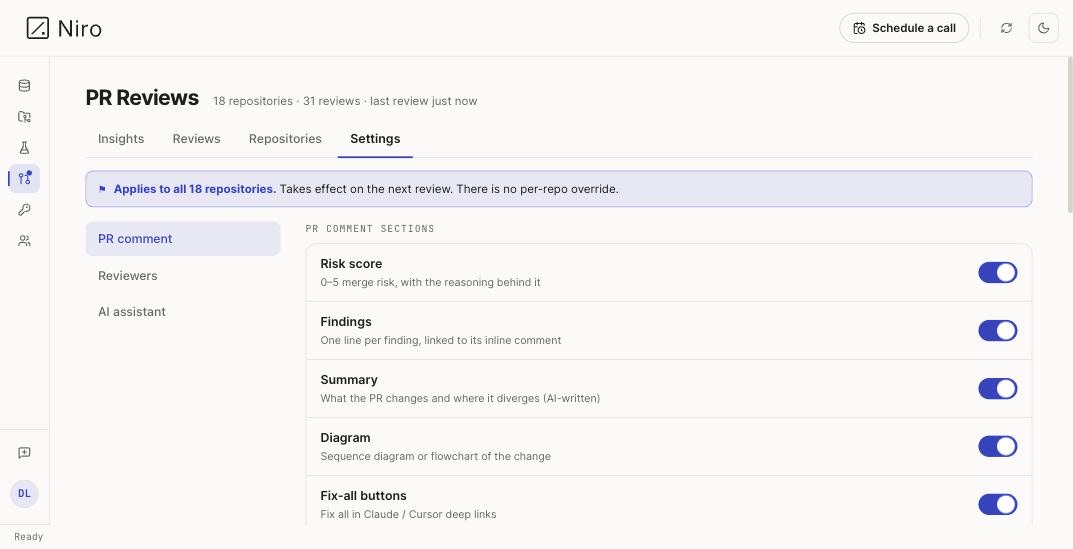
Shape what lands on the PR
Risk score, findings, summary, diagram, fix-all buttons and the fix prompt are each a switch. Pick Advisor to comment only, or Guardian to block the merge on a blocker.
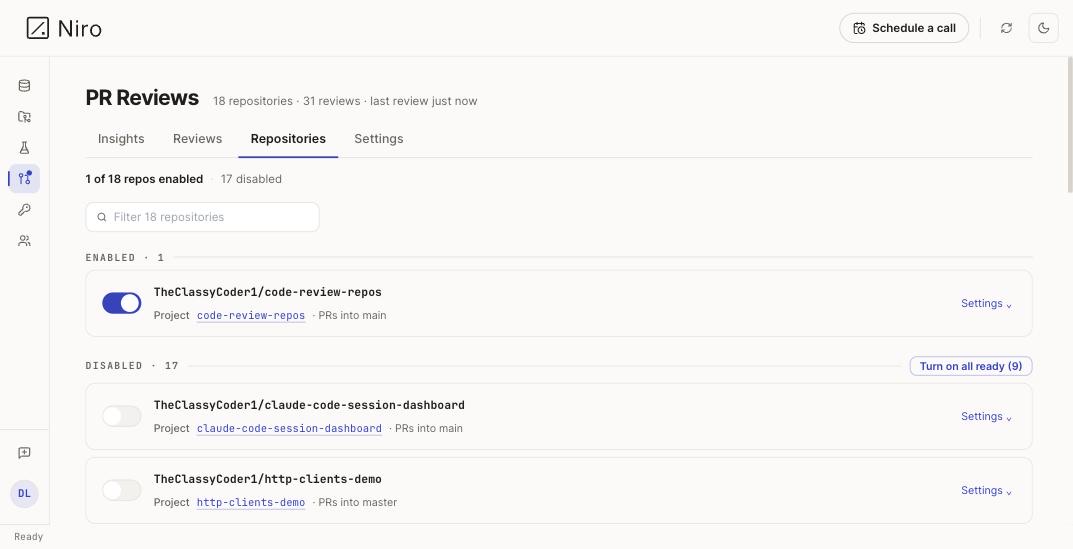
Choose where Niro runs
Each repository is off until you turn it on, with its own project and base branch.
Screenshots are from Niro's review of a sample pull request on 2 October 2026. The live view is from #87, the same change opened a few minutes earlier.
FAQ
Which platforms does PR review support?
GitHub only, for now. Niro installs as a GitHub App on the repositories you choose, rather than as a bot account holding a seat.
Will it flood our pull requests?
Multiple reviewer agents read the diff in parallel, then a verifier tries to refute every finding before delivery. When it is uncertain it leans refuted, because a false alarm costs more than a dropped maybe. Dispute a finding on the PR and it is re-checked against your doubt without folding to it. Every capability is also flag-gated and defaults off, so adoption is a decision rather than a surprise: you turn on the passes that earn their place.
Does this replace human review?
No. It reads the graph behind the diff and reports the call paths a diff view cannot show you, including which of them no test covers. Deciding what to do about them is still a reviewer's job.
Does our diff reach your logs, or a model provider directly?
Neither. No source, no diff content and no prompts are written to logs. Logs carry paths and counts only, a rule written into the service principles rather than bolted on afterwards. Every model call goes through one gateway, so what leaves is auditable in a single place.
Know what a PR breaks before it merges
Install Niro on one repository. Its agents review your next pull request and hand your team the blast radius across every repo you connect.